MSPs are leaving recurring revenue on the table by ignoring CTEM
If you’ve ever delivered a vulnerability assessment, sent the report and watched the engagement end, you’ve experienced the fundamental problem with point-in-time security. You find what’s exposed on one day. Everything that changes the next day is invisible until the next scan. For years, that was acceptable. It isn’t anymore. Cyber insurers across North America are rewriting their underwriting requirements for 2026. Annual questionnaires are being […]
Continuous Threat Exposure Management: Why Cybersecurity Needs to Move Beyond Annual Assessments
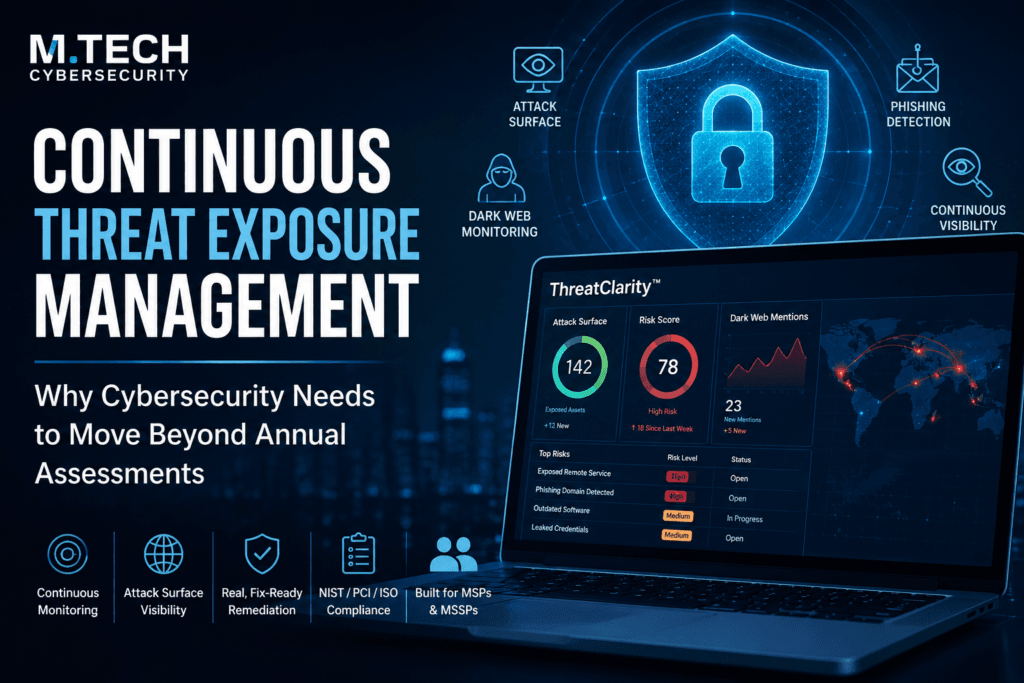
Yet many organizations still rely on security assessments, penetration tests, and vulnerability reports that provide only a periodic snapshot of their cyber exposure. By the time that report reaches decision-makers, the organization’s environment may have already changed. New assets may have been deployed. Employees may have fallen victim to phishing campaigns. A previously secure configuration […]